

 1395 Kundenrezensionen
 Wir sind zuversichtlich von unseren Produkten, die wir bieten keinen Mühe-Produkt-Austausch.


In den letzten Jahren nehmen immer mehr Menschen an der Fortinet FCSS_LED_AR-7.6 Zertifizierungsprüfung teil. Da diese Prüfung kann Ihnen helfen, das Fortinet-Zertifikat zu erhalten, das eine wichtige Grundlage für die Messung Ihrer Fortinet-Kenntnisse ist. Mit dem Fortinet-Zertifikat können Sie ein besseres Leben führen.
Bei ZertSoft bieten wir Ihnen die genauesten und neuesten FCSS - LAN Edge 7.6 Architect Prüfungsmaterialien. Wenn Sie sich auf FCSS_LED_AR-7.6-Prüfung vorbereiten, sind diese Prüfungfragen und -antworten auf ZertSoft absolut Ihr bester Helfer. Mit unseren Fortinet-Studienmaterialien werden Sie in der Lage sein, Fortinet FCSS_LED_AR-7.6 Prüfung beim ersten Versuch zu bestehen. Und Sie brauchen nicht zu viel Zeit auf andere Referenz-Bücher zu verbringen, Sie brauchen nur 20-30 Stunden zu kosten, um unsere Prüfungsmaterialien gut zu erfassen.
ZertSoft ist eine Website, die über eine große Mennge von Fortinet-Prüfungsmaterialien verfügt. Unsere FCSS_LED_AR-7.6 PDF Prüfungsfragen und -antworten, die von erfahrenen Fortinet-Experten geschrieben werden, sind von hoher Qualität und haben angemessenen Preis, viele Kunden haben uns akzeptiert. Die Trefferquote liegt bei 99,9%. Die Test Engine auf ZertSoft kann eine echte Prüfungsumgebung simulieren, auf diese Wiese können Sie die FCSS - LAN Edge 7.6 Architect Prüfung mühlos bestehen.
Wir hoffen, dass wir jedem Kunden qualitativ hochwertigen Service anbieten können. Nachdem Sie FCSS_LED_AR-7.6 Prüfungsmaterialien kaufen, versprechen wir Ihnen einjährigen kostenlosen Update-Service. Damit die Kandidaten zufrieden sind, arbeiten unsere Fortinet-Experten ganz fleißig, um die neuesten Prüfungsmaterialien zu erhalten. Wir überprüfen auch jeden Tag die Aktualisierung. Solange sich die Schulungsunterlagen aktualisieren, senden wir Ihnen die neuesten automatisch in Ihre Mailbox.
Vor dem Kauf können Sie unsere kostenlose Demo zur FCSS - LAN Edge 7.6 Architect Prüfung als Probe downloaden. Sind Sie damit zufrieden, können Sie den Auftrag fortsetzen und vollständige FCSS_LED_AR-7.6 Prüfungsfragen und -antworten kaufen.
100% Geld-zurück-Garantie - Fallen Sie bei der Prüfung durch, geben wir Ihnen eine volle Rückerstattung. Sie brauchen nur die Scan-Kopie ihres Prüfungszeugnis an uns senden. Nach der Bestätigung werden wir Ihnen rückerstatten.
Und es gibt nur zwei Schritte, damit Sie Ihren Auftrag beenden. Wir werden Ihr Produkt in Ihre gültige Mailbox senden. Dann können Sie den Anhang downloaden und die Uterlagen benutzen.
Fortinet FCSS_LED_AR-7.6 Prüfungsplan:
| Thema | Einzelheiten |
|---|---|
| Thema 1 |
|
| Thema 2 |
|
| Thema 3 |
|
| Thema 4 |
|
Referenz: https://training.fortinet.com/local/staticpage/view.php?page=lan_edge_architect_exam
Fortinet FCSS - LAN Edge 7.6 Architect FCSS_LED_AR-7.6 Prüfungsfragen mit Lösungen
Refer to the exhibits.

Examine the firewall policy configuration and SSID settings.
Users trying to connect to the new Guest wireless network should be redirected to an external captive portal, however, these wireless users are not able to see the captive portal login page.
The external captive portal URL has been verified as correct, yet the issue persists.
Which configuration change should fix the problem?
- A. Include the user group guest.portal in the firewall policy.
- B. A firewall policy with the ID 11 is missing to enable the captive-portal-exempt option.
- C. Security mode should be set to WPA2 Enterprise to authenticate through RADIUS.
- D. Add FortiAuthenticator and WindowsAD as exempt sources.
Antwort: B 🗳️
Erklärung: (Nur für ZertSoft-Mitglieder sichtbar)
What is the primary benefit of the LAN Edge solution?
- A. It integrates wired networking with advanced firewall capabilities.
- B. It focuses on enhancing wireless network performance.
- C. It supports scalable and adaptable networking.
- D. It provides centralized management, simplifies operations, and uses AI/ML.
Antwort: D 🗳️
Erklärung: (Nur für ZertSoft-Mitglieder sichtbar)
Refer to the exhibits.


Examine the FortiGate configuration, FortiAnalyzer logs, and FortiGate widget shown in the exhibits.
Security Fabric quarantine automation has been configured to isolate compromised devices automatically. FortiAnalyzer has been added to the Security Fabric, and an automation stitch has been configured to quarantine compromised devices.
To test the setup, a device with the IP address 10.0.2.1 that is connected through a managed FortiSwitch attempts to access a malicious website. The logs on FortiAnalyzer confirm that the event was recorded, but the device does not appear in the FortiGate quarantine widget.
Which two reasons could explain why FortiGate is not quarantining the device? (Choose two.)
- A. The malicious website is not recognized as an indicator of compromise (IOC) by FortiAnalyzer.
- B. The SSL inspection should be set to deep-Inspection.
- C. The threat detection services license is missing or invalid under FortiAnalyzer.
- D. The IOC action should include only the FortiSwitch in the quarantine.
Antwort: A,C 🗳️
Erklärung: (Nur für ZertSoft-Mitglieder sichtbar)
APs have been manually configured to connect to FortiGate over an IPsec network, and FortiGate successfully detects and authorizes them. However, the APs remain unmanaged because FortiGate is unable to establish a CAPWAP tunnel with them. What configuration change can resolve this issue and enable FortiGate to establish the CAPWAP tunnel over the IPsec connection?
- A. Assign a custom AP profile for the remote APs with the set mpls-connection option enabled.
- B. Configure a static route on FortiGate to reach the APs over the IPsec tunnel.
- C. Decrease the CAPWAP tunnel MTU size for APs to prevent fragmentation.
- D. Upgrade the FortiAP firmware image to ensure compatibility with the FortiOS version.
Antwort: A 🗳️
Erklärung: (Nur für ZertSoft-Mitglieder sichtbar)
Refer to the exhibits.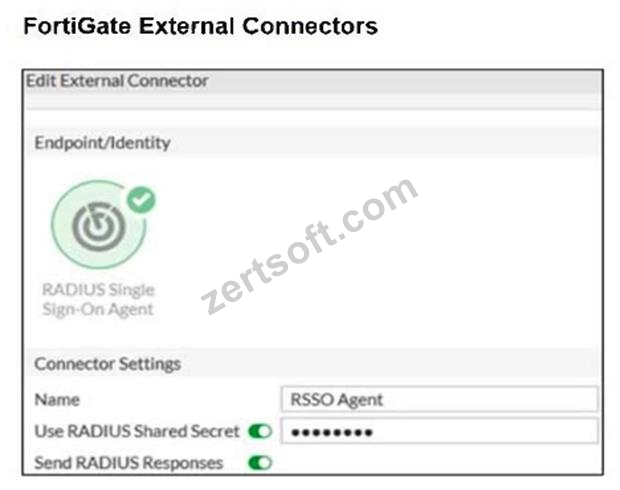
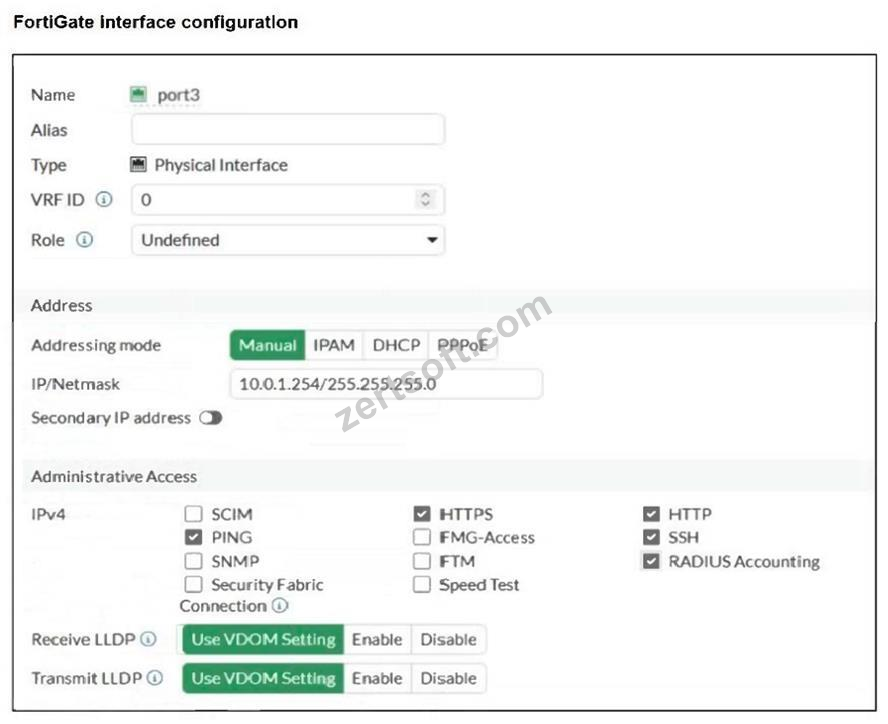
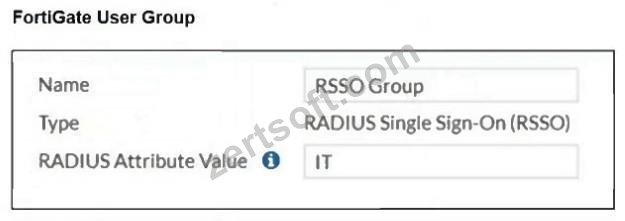

A network administrator is configuring RADIUS single sign-on (RSSO) on FortiGate to dynamically assign users to specific user groups based on RADIUS accounting messages.
Which two configuration steps are required to ensure RSSO user group matching work correctly?
(Choose two.)
- A. Set the rsso-endpoint-attribute to define which RADIUS attribute will be used to extract username.
- B. Enable the RSSO agent service on FortiGate to actively poll RADIUS servers for authentication requests.
- C. Configure the sso-attributein the RSSO agent settings to specify which RADIUS attribute will be used for group matching.
- D. Configure FortiGate to send RADIUS authentication requests instead of relying on accounting messages.
Antwort: A,C 🗳️
Erklärung: (Nur für ZertSoft-Mitglieder sichtbar)
Seite 1 von 22 wird angezeigt.
Fragen 1-5 von 108 werden angezeigt.


Langhans -
Ich bestand die FCSS_LED_AR-7.6 Prüfung in der letzten Woche. Ich benutzte die Studienmaterialien von ZertSoft. Ihre Studienführung hilft mir, viel Zeit gespart zu haben. Ich lernte in nur 30 Stunden. Vielen Dank!